Cyberattacks are becoming faster, attack surfaces are expanding, and the interconnections are growing more complex. It is therefore crucial not only to detect threats early on, but also to draw the right conclusions from numerous signals. As one of the leading SOC providers in the DACH region, InfoGuard combines 24/7 Managed Detection & Response (MDR) with Managed Risk Exposure (MRE), AI-powered analytics, and human expertise — for proactive and risk-based cyber defense.
24/7 SOC service: 3 guarantors of modern cyber defence and maximum cyber security
Whether as a Managed SOC or Co-Managed SOC, our approach combines continuous monitoring and rapid response with proactive risk management. This allows us not only to detect ongoing attacks but also to provide transparency regarding actual attack surfaces and prioritize risks before they escalate into security incidents. Three key success factors set our SOC services apart:
- Staffed 24/7: Our Cyber Defense Centers are staffed around the clock by experienced SOC and CSIRT experts. AI-powered analytics help them analyze cyber threats more quickly, identify patterns, and prioritize risks. In the event of an incident, our specialists are immediately available to respond.
- MDR meets Managed Risk Exposure (MRE): Our open XDR architecture integrates existing security technologies and provides comprehensive visibility. Managed Risk Exposure expands traditional Detection & Response to include a proactive perspective: Actual attack surfaces are identified, risks are prioritized strategically, and security measures are implemented where they have the greatest impact.
- Data Sovereignty and AI by Design: At InfoGuard, AI is used in a controlled and traceable manner. Data protection, governance, traceability, and compliance are taken into account from the very beginning. LLM data processing is tailored to your requirements for data sovereignty and compliance—whether in the EU, Switzerland, or on dedicated AI hardware in your own country.
Take advantage of the synergy between experienced professionals, AI-powered analytics, cutting-edge technology, and established processes—for cyber defense that doesn’t just start when an alert is triggered. Everything at a glance:
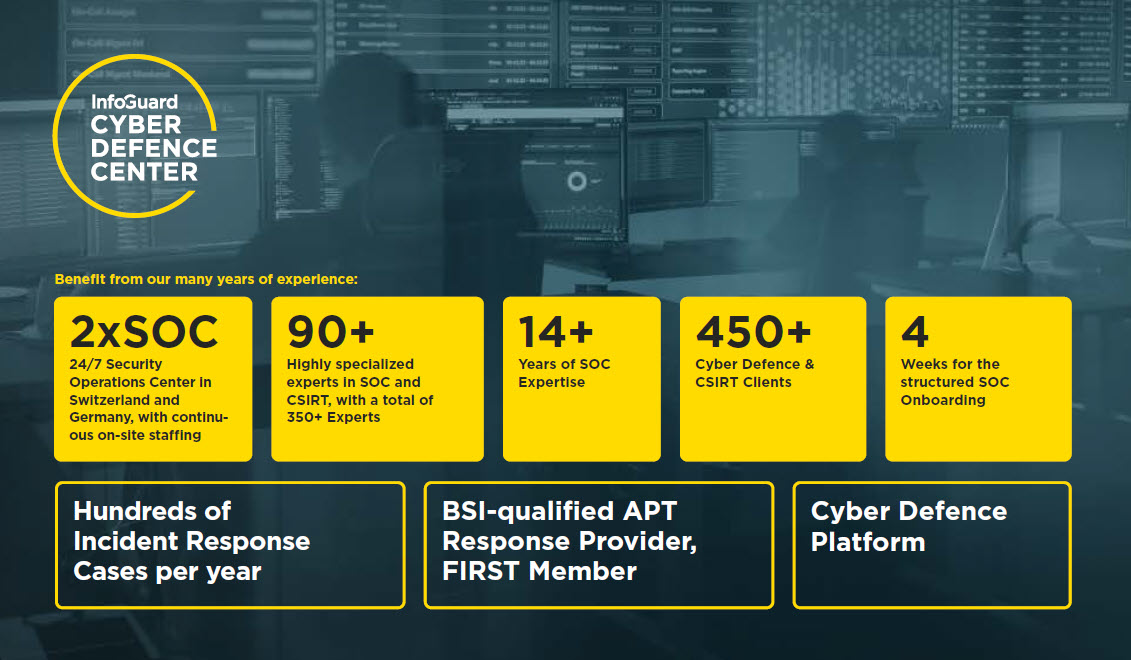
- 24/7 fully staffed Cyber Defense Centers in Switzerland and Germany
- Over 90 SOC and CSIRT experts working in 24/7 live operations
- More than 14 years of experience and expertise in the SOC field
- Over 450 SOC and CSIRT clients
- Managed Detection & Response (MDR) and Managed Risk Exposure (MRE) for reactive and proactive cyber defense
- AI-powered analytics for faster analysis and prioritization of security incidents
- AI by Design for controlled AI deployment with data protection, governance, traceability, and compliance
- High data sovereignty with LLM data processing tailored to requirements in the EU, Switzerland, or on dedicated AI hardware in the customer’s own country
- Open XDR architecture for integrating existing security technologies
- ISO 27001-certified SOC and ISAE 3000 Type 2 attested
Interested? Talk to our experts about the right SOC and MDR solution for your needs — from 24/7 detection and response to proactive management of your actual cyber risks.
InfoGuard Incident Response Retainer Service –
act quickly and purposefully in an emergency
A successful cyberattack can never be completely ruled out. What matters most is how quickly you can get back up and running. The InfoGuard CSIRT (Computer Security Incident Response Team) provides immediate and professional support in an emergency—around the clock. This ensures that experienced incident response specialists are at your side exactly when every minute counts.